Introduction
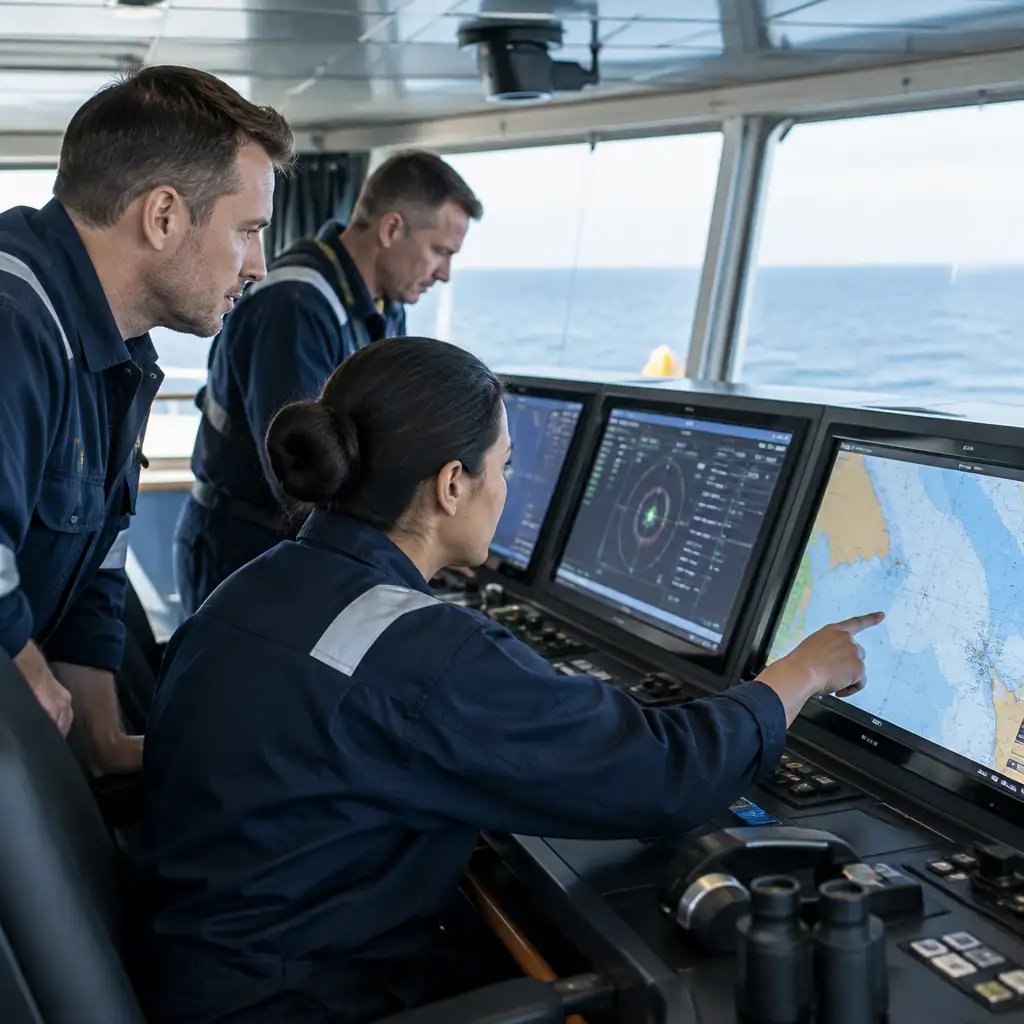
Operational technology (OT) and industrial control systems (ICS) are increasingly present on small and medium commercial vessels. Propulsion controls, electronic chart display and information systems (ECDIS), automatic identification systems (AIS), and onboard networks are essential for safe operations but also introduce new classes of risk. Owners and operators must treat these systems as integral to vessel safety rather than separate IT issues.
This article explains why OT/ICS vulnerabilities matter for maritime safety and operational continuity. Threats can originate from inadequate configuration, delayed patching, insecure remote access, or human error. On small commercial vessels—where crew size and technical resources are limited—single-point failures or compromise of a control system can escalate rapidly to navigation or propulsion incidents with safety and compliance implications.
Practical, prioritized mitigations can reduce risk without expensive retrofits. The guidance that follows focuses on threat scenarios relevant to propulsion, ECDIS, AIS, and onboard networks, and outlines a mix of technical and operational controls that integrate with existing safety management systems (SMS). Compliance considerations and incident response planning are also included to support vessel safety, regulatory compliance, and resilience.
Common OT/ICS Vulnerabilities on Small Commercial Vessels
Small commercial vessels often combine legacy control hardware with modern digital navigation aids. Common vulnerabilities include default or weak credentials on control units, unpatched firmware in propulsion controllers or ECDIS, misconfigured network services, and unsecured remote access paths used for vendor maintenance. Many vessels also have flat networks that allow lateral movement from a compromised laptop to critical systems.
Hardware and software diversity increases complexity: proprietary PLCs, older GPS receivers, and multifunction displays from different manufacturers may lack standardized security features. In addition, operational practices—such as charging personal devices on bridge networks or connecting contractor laptops without vetting—can introduce malware or create unauthorized access points.
Awareness of these vulnerabilities is the first step. Practical risk reduction begins by inventorying OT assets, identifying critical control points, and documenting network topology so that appropriate segmentation and controls can be prioritized.
Threat Scenarios: Propulsion, ECDIS, AIS, and Network Attacks
Scenario 1 — Propulsion control compromise: A vendor maintenance laptop with outdated antivirus is plugged into the engine control network for diagnostics. Malware executes and interferes with engine governor signals, causing erratic RPM behavior and a loss of precise speed control while transiting a crowded channel. This creates collision and grounding risk and may trigger emergency responses.
Scenario 2 — ECDIS tampering or data loss: A corrupt update or successful ransomware attack disables ECDIS during a coastal approach. With charting unavailable, bridge crew revert to paper backups and radar, but unfamiliar harbor channels increase workload and reduce margin for error—especially for smaller crews with limited local knowledge.
Scenario 3 — AIS manipulation and spoofing: Spoofed AIS data or GPS spoofing can present false targets or mislead position reporting, complicating collision avoidance and traffic separation compliance. While AIS is not a primary navigation system, its manipulation can degrade situational awareness and influence bridge decision making.
Prioritized Technical Controls for Immediate Risk Reduction
Network segmentation is the single most effective technical measure for small vessels. Separate critical OT functions (propulsion controllers, ECDIS, AIS) from administrative and guest networks. Enforce physical or logical separation so that a compromised laptop or crew device cannot directly access propulsion or navigation equipment. Implement strict firewall rules limiting protocols and endpoints permitted between network segments.
Patch and configuration management are essential. Maintain an asset register with firmware and software versions, and prioritize patching for devices that affect vessel safety. Where vendor-supplied patches are unavailable, apply compensating controls such as isolating the device or increasing monitoring. Enable secure configurations: disable unused services, change default credentials, and apply least privilege on administrative interfaces.
Additional technical controls include application allowlisting for critical workstations, multi-factor authentication for remote access, logging and intrusion detection tailored to maritime OT, and offline backups for navigation data and system configurations. Where possible, implement read-only or checksum-verified chart storage for ECDIS to mitigate corruption and ransomware risks.
Operational Measures: Crew Training, Access Control, and Procedures
Technical controls must be combined with practical operational measures. Crew cybersecurity training should be role-based: bridge teams need guidance on recognizing GPS anomalies, verifying chart integrity, and safe use of portable devices; engineers need protocol for vendor access to propulsion networks. Regular drills that simulate partial loss of ECDIS or degraded propulsion control help crews practice failover to manual procedures and verify competency.
Access control procedures reduce risk from third parties and contractors. Require vetted and updated maintenance credentials, use jump hosts or intermediary computers with strict controls for vendor connections, and document all remote access sessions. Maintain an equipment log for any external device connected to the vessel network and enforce a policy for scanning and approval before connection.
Administrative controls include strict password policies, defined roles for system administration, and a change-management process for software updates. Linking these procedures to existing vessel procedures—bridge checklists, maintenance logs, and permit-to-work systems—keeps cybersecurity measures practical and enforceable during normal operations.
Integrating Cyber Risk into Safety Management Systems
OT/ICS risk should be treated as a safety hazard within the existing Safety Management System (SMS). Update SMS hazard registers and risk assessments to include cyber impacts on navigation and propulsion. Assign responsibilities for OT risk owners, define acceptable residual risk levels, and include cybersecurity in routine SMS internal audits to validate controls and compliance.
Incident reporting and corrective action processes in the SMS should explicitly cover cyber incidents. Establish clear procedures for reporting anomalies, preserving forensic data, and escalating to shore-based technical support. Including cyber scenarios in SMS safety drills aligns technical response with broader emergency response and ensures bridge and engineering teams coordinate effectively.
For guidance on regulatory expectations and formal compliance pathways, operators should reference maritime compliance resources and align OT controls with applicable regulatory frameworks. Where certification or statutory audits intersect with electronic navigation and safety systems, documenting SMS integration provides evidence of a systematic approach to risk reduction. For support aligning OT programs with regulatory obligations, consider engaging maritime compliance services early in program development. maritime compliance services
Incident Response, Recovery, and Compliance Considerations
Incident response plans should be pragmatic and commensurate with vessel size. Elements include detection and triage procedures, isolation steps to contain compromised segments, backup navigation and propulsion procedures, communication templates for masters and shoreside managers, and evidence preservation for later investigation. Establish thresholds for when to cease operations, seek tug support, or call port authorities based on degraded capabilities.
Recovery planning includes validated backups for ECDIS charts and configuration files for control systems, tested restoration processes, and vendor contacts for authenticated support. Regular exercises that simulate ransomware or ECDIS failure help verify the recovery timeline and identify gaps. Documenting these exercises within the risk management framework supports continuous improvement and provides material for compliance reviews.
Compliance considerations vary by flag and trading area but commonly involve demonstrating risk assessments, documented procedures, and training records. Integrating OT risk into existing marine risk assessments strengthens compliance posture and can be supported by maritime consulting services for program design, audits, and gap analysis. For practical program development and incident planning support, operators can engage specialized consulting resources. marine risk assessments and maritime consulting services can assist with translating technical controls into operational policy and SMS documentation.
Frequently Asked Questions
Q: What are the first steps for small vessel operators concerned about OT risk?
A: Begin with an asset inventory and basic network diagram to identify critical systems. Implement immediate measures such as network segmentation, change default credentials, and establish a simple patch and backup cadence. Combine these with crew briefings and a documented plan for vendor access.
Q: How can an operator balance operational needs for remote vendor access with security?
A: Use controlled access methods: require vetted jump hosts, restrict access to specific IPs and ports, mandate multi-factor authentication, and log all sessions. Pre-approve vendor visits and scan external devices before connecting them to OT networks. Maintain a documented permit process and supervisory oversight during maintenance activities.
Q: Are there regulatory requirements for cybersecurity on small commercial vessels?
A: Regulatory expectations are evolving. Many administrations expect operators to manage cyber risks as part of safety and compliance obligations. Documenting risk assessments, training, incident response planning, and integration of cyber risk into the SMS demonstrates a systematic approach aligned with maritime compliance expectations.
Effective risk management begins with identifying hazards before incidents occur. Marine Safety Consultants offers practical guidance for vessel operators, facility owners, and maritime organizations. Contact us at 508-996-4110 or tom@marinesafetyconsultants.com.